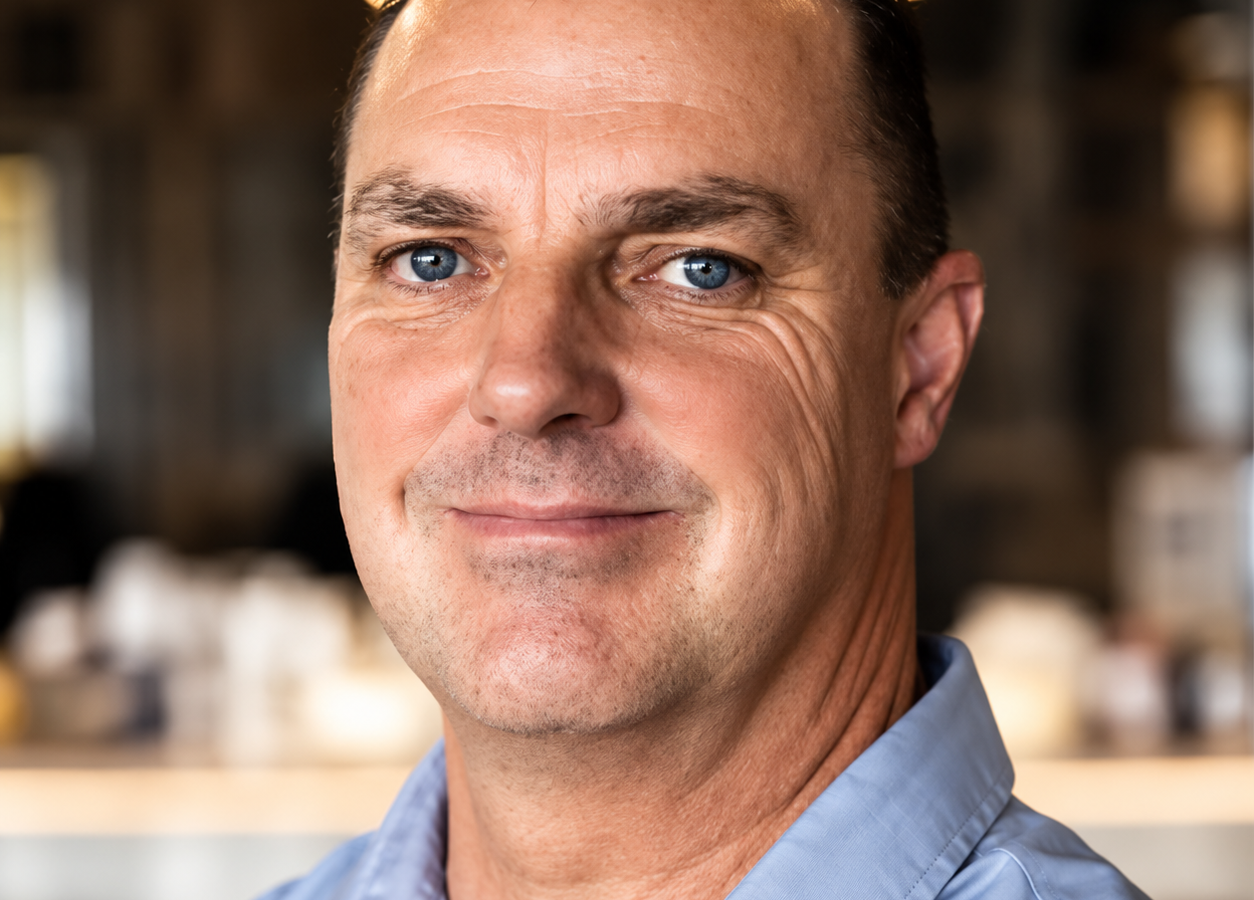
Riaan van Jaarsveld, Director of RiXForensica
As cyber incidents remain the world’s top business risk, forensic experts urge organisations to move beyond prevention and prepare for the realities of investigation, evidence preservation and recovery.
For years, cybersecurity conversations have focused on firewalls, passwords and phishing awareness. However, according to forensic investigations specialist RiXForensica, organisations may be overlooking a critical reality: the question is no longer whether a cyber-incident will occur, but whether organisations are prepared for what happens afterwards.
As organisations mark Cybersecurity Awareness Month, new global and local research points to a growing disconnect between cyber prevention efforts and cyber response readiness.
Number one risk for the fifth consecutive year
Cyber incidents remain the number one business risk in South Africa, Africa and globally, according to the Allianz Risk Barometer 2026, ranking ahead of business interruption, regulatory change and natural catastrophes for the fifth consecutive year. The report found cyber risk to be the leading concern for organisations of all sizes and across regions worldwide, including South Africa, Africa and the Middle East.
Cyber risk accelerating at a pace that organisations are struggling to match
At the same time, the World Economic Forum Global Risks Report 2026 and Global Cybersecurity Outlook 2026 warn that artificial intelligence, geopolitical tension, cybercrime syndicates and increasingly complex digital ecosystems are accelerating cyber risk at a pace that many organisations are struggling to match.
“Many organisations continue to approach cybersecurity primarily as a technology issue,” says Riaan van Jaarsveld, Director of RiXForensica.
“The reality is that today’s cyber incidents can rapidly become legal, operational, financial and reputational crises. Organisations need to think beyond prevention and begin building forensic readiness so that they can investigate, respond to and recover from incidents effectively.”
South Africa is an increasingly attractive target
South Africa’s advanced digital economy makes it one of the continent’s most attractive targets for cybercriminals.
According to the INTERPOL Africa Cyberthreat Assessment Report 2025, South Africa remains among the most targeted countries in Africa for ransomware attacks, particularly within the finance and government sectors. The report also highlights growing threats from business email compromise, phishing campaigns and attacks against critical infrastructure.
The financial consequences are becoming increasingly severe.
R44.2 million: Average data breach costs in South Africa
Research from IBM’s Cost of a Data Breach Report 2025 found that the average data breach in South Africa costs approximately R44.2 million, while the financial services sector experiences average breach costs exceeding R70 million. Detection and escalation activities, business disruption and post-breach response account for the largest proportion of those losses.
R1 billion: Consumer losses
Meanwhile, research cited in the KnowBe4 African Cybersecurity & Awareness Report 2025 found that South African consumers lost more than R1 billion through digital banking and mobile application-related crime during 2023. The report highlights the growing role of social engineering, phishing, impersonation and AI-enabled fraud in driving cybercrime across the country.
The five industries facing the greatest cyber exposure
Drawing on international and local cyber risk reporting, RiXForensica believes five sectors face particularly heightened cyber exposure due to the value of their data, operational importance and potential reputational consequences.
1. Financial Services
Banks, insurers, wealth managers and investment firms remain primary targets because of the direct financial gain available to attackers and the significant volumes of sensitive customer information they manage.
IBM’s research found that South Africa’s financial sector experiences the highest average breach costs of any industry.
2. Government and Public Sector
Government departments, municipalities and state-owned entities hold significant volumes of personal, financial and strategic information while also providing essential services to citizens.
Recent cyber incidents affecting public institutions demonstrate the potential for widespread disruption when attacks are successful.
3. Healthcare
Medical institutions increasingly face ransomware, and data theft risks due to the high value of patient records and the urgency with which healthcare services must be restored following disruption.
Internationally, healthcare remains one of the sectors most vulnerable to operational and reputational damage arising from cyber incidents.
4. Professional Services
Law firms, accounting practices, engineers, consultants and corporate advisors often possess highly confidential information relating to litigation, mergers and acquisitions, intellectual property and commercial transactions.
These organisations may not always view themselves as cyber targets, despite holding information that is valuable to both criminal and state-sponsored actors.
5. Critical Infrastructure, Manufacturing and Logistics
Increasing digitalisation has connected operational technology and business systems in ways that create new opportunities for cybercriminals to disrupt supply chains, production facilities and essential services.
Reputation damage may exceed technical losses
According to the Aon’s Global Cyber Risk Report 2025, organisations that experienced significant cyber-related reputation events suffered an average 27% decline in shareholder value. The report identified ransomware and malware incidents as among the most likely cyber events to evolve into broader reputational crises.
“The biggest cost of a cyber-incident is often not the technology recovery process,” says van Jaarsveld.
“It is the loss of trust, stakeholder confidence, business interruption, legal exposure and long-term reputational impact that follows. These are consequences that boards and executive teams can no longer afford to treat as secondary considerations.”
From cyber awareness to forensic readiness
RiXForensica believes the next frontier in organisational resilience is forensic readiness: the ability to preserve evidence, establish facts, support investigations and make informed decisions immediately following a cyber-incident.
This includes ensuring organisations can:
- Preserve digital evidence from the moment an incident is identified.
- Determine how attackers gained access.
- Establish what information has been compromised.
- Support insurance, litigation and regulatory processes.
- Minimise business disruption.
- Protect organisational reputation through evidence-based response strategies.
“Most organisations have disaster recovery plans and business continuity frameworks,” says van Jaarsveld.
“Far fewer have clear processes for preserving evidence, conducting forensic investigations or managing the legal and reputational consequences of a cyber-incident. In today’s environment, those capabilities are becoming essential.”
As cyber risk continues to dominate global business concerns, RiXForensica is urging organisations to use Cybersecurity Awareness Month not only to strengthen prevention, but also to assess their readiness to investigate, respond to and recover from the cyber incidents that increasingly define today’s risk landscape.